We may earn a referral fee at no additional cost to you when you shop through the links on this page.
Ubuntu 26.04 LTS (Resolute Raccoon), released April 2026, is the latest long-term support release with security updates guaranteed until April 2031 (extendable to 2036 with Ubuntu Pro). It ships with Nginx 1.28 and PHP 8.5, making it an ideal choice for modern web hosting….
The following steps cover installing the Nginx web server, configuring UFW firewall rules for web traffic, verifying the service, and setting up a server block for your domain.
Prerequisites
Before you begin, ensure you have a server running Ubuntu 26.04 (Resolute Raccoon) with a non-root user that has sudo privileges, plus SSH or console access. If you are setting up a server for the first time, see our initial server setup guide for Ubuntu 26.04 (Resolute Raccoon).
Installing Nginx
Update the local package index to ensure the package manager has the latest information about available software versions, then install the nginx package:
sudo apt update && sudo apt install -y nginxThis installs Nginx 1.28 from the Ubuntu 26.04 (Resolute Raccoon) repositories. The server starts automatically after installation.
Adjusting the Firewall
Before testing Nginx, configure a firewall to allow external access to web ports while restricting other traffic. This guide uses UFW (Uncomplicated Firewall), which works identically on Ubuntu and Debian.
If UFW is not already installed:
sudo apt install -y ufwAllow SSH connections first (if connecting remotely):
sudo ufw allow OpenSSHAllow Nginx through the firewall:
sudo ufw allow 'Nginx Full'Enable the firewall:
sudo ufw enableIf you see “Command may disrupt existing ssh connections. Proceed with operation (y|n)?” Press y and Enter.
Verify the status:
sudo ufw statusYou should see Nginx listed as well as OpenSSH if you’re using it.
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere
Nginx Full                 ALLOW       Anywhere
OpenSSH (v6)               ALLOW       Anywhere (v6)
Nginx Full (v6)            ALLOW       Anywhere (v6)
Verifying the Installation
Nginx starts automatically after installation. Confirm the service is active:
sudo systemctl status nginxYou should see active (running) in the output.
Test locally or from a remote machine:
hostname -I for your local IP, or curl -4 icanhazip.com for your public IP on a VPS. curl http://localhost
# or from remote:
curl http://your_server_ipIf you see HTML output in the response, the install was successful.
If you have access to a browser, you should see the default Nginx welcome page displaying ‘Welcome to nginx!’.
The default Nginx welcome page is located at /var/www/html/index.nginx-debian.html.
Managing the Nginx Service
Essential systemd commands for managing Nginx:
| Action | Command | Notes |
|---|---|---|
| Stop | sudo systemctl stop nginx | Halts the service completely |
| Start | sudo systemctl start nginx | Starts if stopped |
| Restart | sudo systemctl restart nginx | Full restart (brief downtime) |
| Reload | sudo systemctl reload nginx | Graceful reload (preferred for config changes) |
| Enable on boot | sudo systemctl enable nginx | Auto-start after reboot |
| Test config | sudo nginx -t | Validate config before reload |
sudo nginx -t before reloading. A config syntax error will prevent Nginx from starting, potentially taking your site offline. Important File Locations
Key paths to know for managing Nginx on Ubuntu 26.04 (Resolute Raccoon):
- Default Web Root:
/var/www/html— Your web content goes here. - Main Configuration:
/etc/nginx/nginx.conf— Global configuration file. - Server Blocks:
/etc/nginx/sites-available/— Per-site configurations. - Enabled Sites:
/etc/nginx/sites-enabled/— Symlinks to active configurations. - Access Log:
/var/log/nginx/access.log— All requests to your server. - Error Log:
/var/log/nginx/error.log— Errors and diagnostics.
Setting Up a Server Block
To serve content for your domain instead of the default page, configure a server block (Nginx’s equivalent of Apache’s virtual host).
/etc/hosts file on your client machine. Create a Directory for Your Site
sudo mkdir -p /var/www/example.comCreate a Sample Page
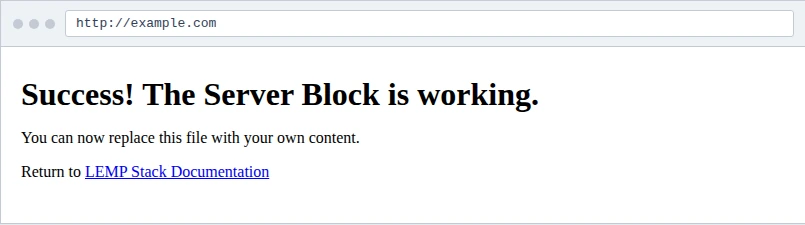
echo '<html><head><title>Success</title></head><body><h1>Success! The Server Block is working.</h1><p>You can now replace this file with your own content.</p><p>Return to <a href="https://devanswers.net/series/lemp-stack/">LEMP Stack Documentation</a></p></body></html>' | sudo tee /var/www/example.com/index.htmlSet Permissions
Assign ownership to the web server user and configure group permissions:
sudo chown -R www-data:www-data /var/www/example.com
sudo chmod -R 775 /var/www/example.com
sudo chmod -R g+s /var/www/example.com
Add your user to the www-data group so you can modify files without sudo:
sudo usermod -aG www-data $USERid. Create the Server Block Configuration
sudo nano /etc/nginx/sites-available/example.comPaste the following configuration (replace example.com with your domain):
server {
    listen 80;
    listen [::]:80;

    server_name example.com www.example.com;
    root /var/www/example.com;
    index index.html index.htm;

    location / {
        try_files $uri $uri/ =404;
    }

    access_log /var/log/nginx/example.com-access.log;
    error_log /var/log/nginx/example.com-error.log;
}
Save and exit (press CTRL + X, press Y, then press ENTER)
try_files directive tells Nginx to look for the exact URI first, then a directory, and return a 404 if neither exists. This prevents directory listing and handles clean URLs. Enable the Site and Reload Nginx
Create a symlink to enable your server block, remove the default site symlink, and reload Nginx:
sudo ln -s /etc/nginx/sites-available/example.com /etc/nginx/sites-enabled/
sudo rm /etc/nginx/sites-enabled/default
sudo nginx -t && sudo systemctl reload nginxa2ensite or a2dissite commands. You manage sites by creating and removing symlinks in /etc/nginx/sites-enabled/ manually. Test It
Visit http://example.com in your browser. As long as your domain’s A record points to your server’s IP, you should see the sample page.
Conclusion
You now have Nginx 1.28 running on Ubuntu 26.04 (Resolute Raccoon) with a configured server block.
Your server is ready for the next steps: installing a database server (MariaDB or MySQL), adding PHP-FPM for dynamic content, or deploying your application. For production sites, consider adding SSL/TLS encryption with Let’s Encrypt.

Comments